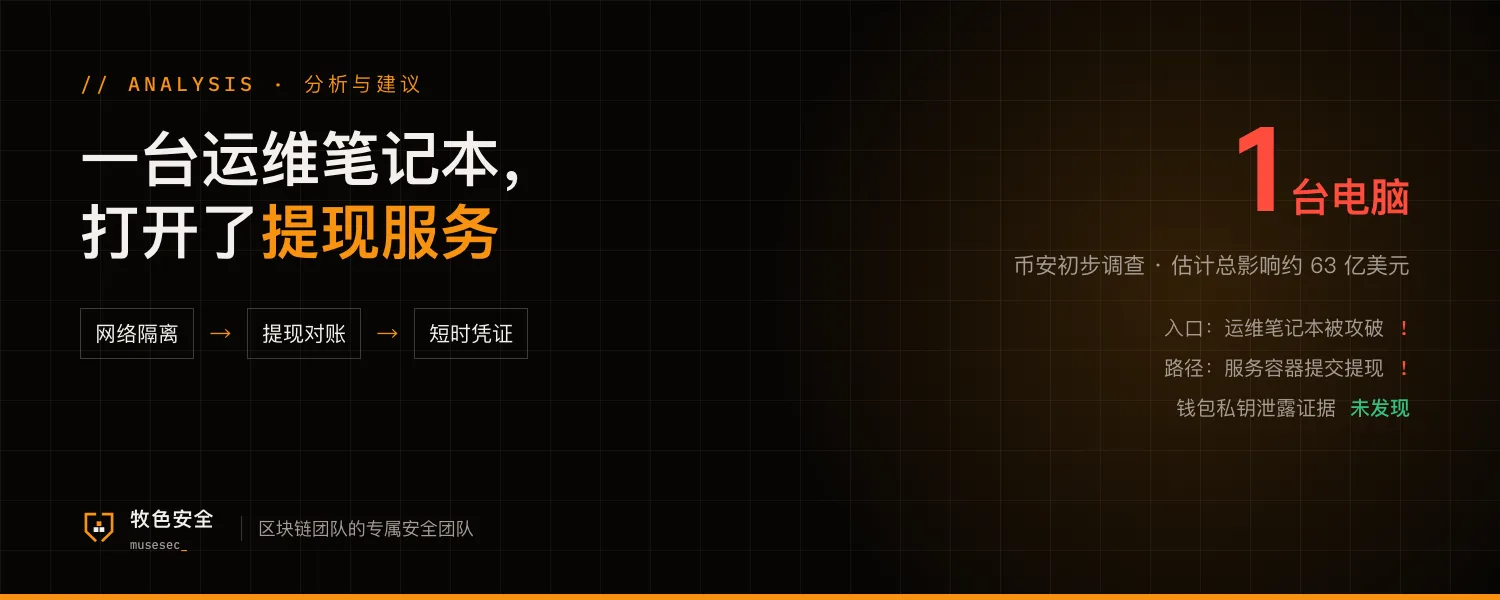
In an update on October 30, Binance said its initial investigation suggests the incident may involve a compromised DevOps engineer's laptop, which let the attacker reach a service container and submit unauthorized withdrawal transactions. Binance says it has found no evidence of a wallet private key leak.
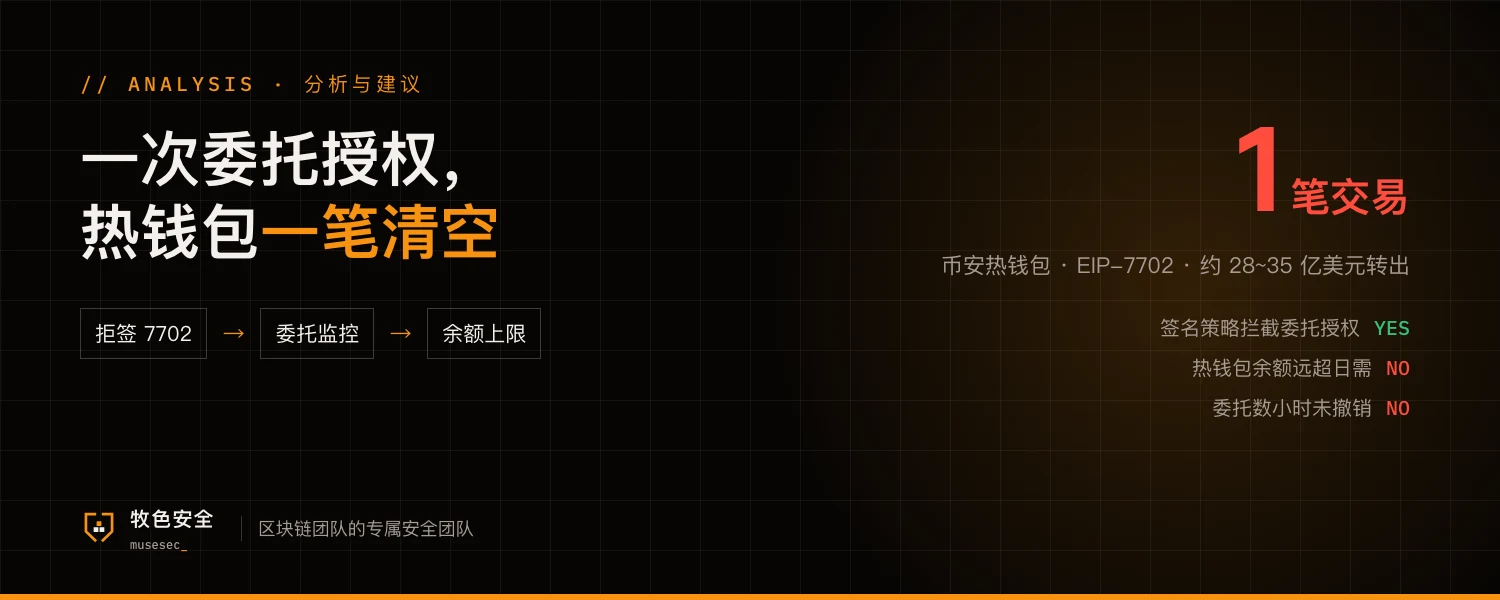
Binance estimates the total impact at around $6.3B, with about $3B frozen on-chain so far. Deposits and withdrawals remain suspended, losses will be covered by SAFU and company funds, and a detailed technical post-mortem will follow. According to researchers, the attacker spent several hours preparing on-chain before the main transfers. Our earlier article, "Binance Hot Wallet Swept in One Transaction via EIP-7702 Delegation", covers how the funds left.
Where small teams are exposed
Process
Strong key custody does not help if a service can still submit transactions to the signer. Many signing policies only check that a request comes from an internal service, and never check that it matches a real withdrawal request or a sensible amount.
Risk
An ops engineer's laptop usually holds live sessions for VPN, cloud consoles, Kubernetes and bastion hosts. One phishing email or piece of malware turns it into an entry point to production. In a small team, one person often runs servers, CI and the wallet service.
Privileges
If nothing sits between a laptop and a container that can submit withdrawals, no second approval and no network boundary, then one compromised laptop is a compromised treasury.
Five things you can do now
- List every system and container that can send transactions to your signer or hot wallet. Isolate them from the office network and staff laptops, and require bastion access with audit logs
- Add independent checks on the signing side: every withdrawal must match a request in the business system, and anything over per-transaction or time-window limits is held for a second person to approve
- Move engineers' production access to short-lived credentials that are requested on demand and expire. Do not keep cloud console sessions, kubeconfigs or production SSH keys on laptops long term
- Run EDR on every machine that can reach production, control browser extensions and software sources, and alert on unusual logins and new devices
- Rehearse a "compromised ops laptop" scenario: how fast you detect it, who revokes credentials and halts outflows, and whether your logs can rebuild the attack path
The preliminary cause, the absence of evidence of a key leak, the estimated impact and the frozen amount come from Binance's October 30 update, which says the incident "may involve" the laptop; its technical post-mortem will be the reference. There is no official attribution yet, so this article does not name an attacker. This article does not cover attack details.
Sources
- Binance: security incident update (2026-10-30) ↗
- PANews: Binance says incident may involve a compromised DevOps engineer laptop (Chinese) ↗
- Bloomingbit: Binance Estimates Security Breach Losses at $6.3 Billion ↗
- CoinDesk: Live updates: Binance confirms security breach ↗
Also on X · Oct 30, 2026: View the original post on X ↗