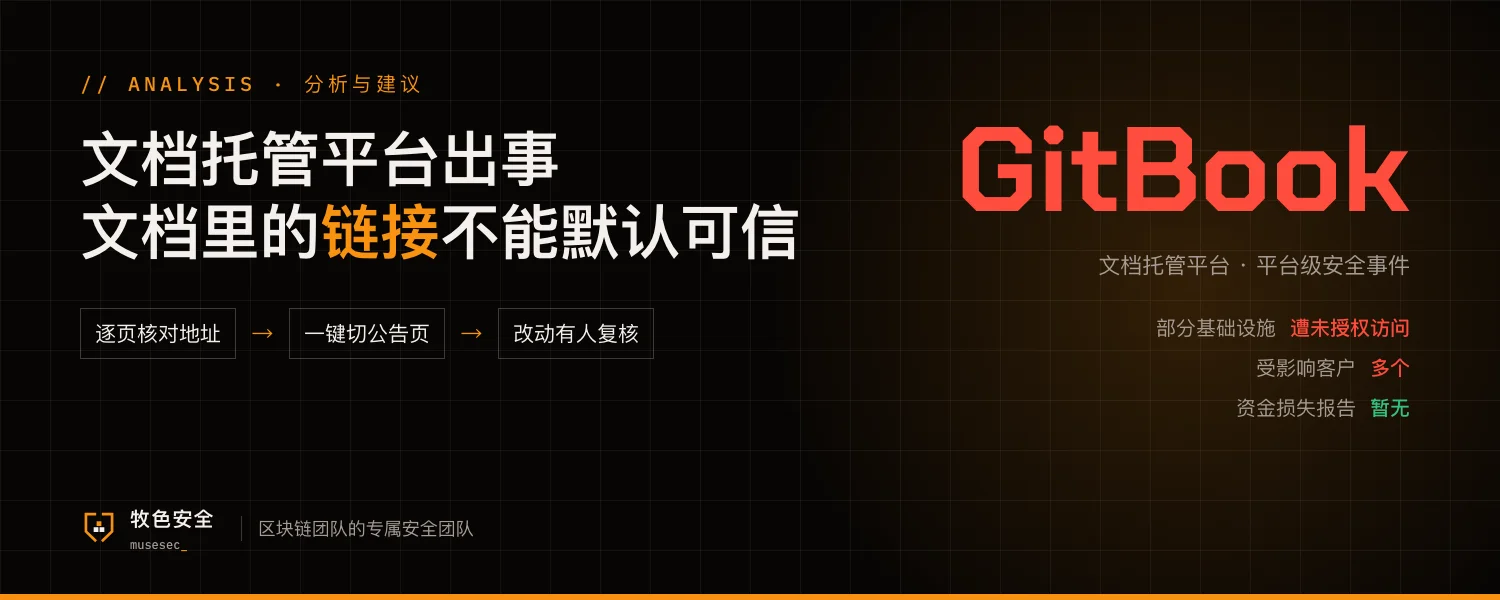
Docs hosting platform GitBook detected unauthorized access to parts of its infrastructure on November 2. It calls this a platform-wide issue affecting a number of customers, says the incident has been contained, and took some services offline as a precaution. Whether customer data was affected is still under investigation, and a full post-incident report will follow. As of the evening of November 3 (UTC+8), its status page showed the app and public content back online and under monitoring.
The same day, perpetual futures platform trade[XYZ] reported unauthorized activity on its GitBook-hosted docs and, even after restoring them, told users not to click links in the docs while it investigates. PancakeSwap said its own docs were not compromised, took them offline as a precaution, and then moved them from GitBook to infrastructure it controls. No fund losses have been reported, and neither the attack method nor the list of affected customers has been disclosed.
Where small teams are exposed
Process
Docs sites are often treated as "where we write explanations," so edits skip review and the site never makes it onto the security checklist. Users treat it as an official source and copy contract addresses, app links and deposit instructions straight from it.
Risk
Once a docs site is altered, an attacker does not need to touch your contracts or servers. Swapping a single link or address can send users to a wallet drainer, under your own domain.
Privileges
Docs platforms tend to collect editors: former staff, freelance writers, early team members. And when the hosting platform itself is breached, clean permissions on your side will not stop it.
Five things you can do now
- Open your docs site today and check every contract address, app link, download link and deposit instruction. If anything looks wrong, take it offline first and investigate after
- Prepare a switch that lets you point your docs domain to an announcement page on your main site within minutes
- Treat your website or app as the source of truth for contract addresses and official links, and say so on the docs homepage. Do not publish them only on a third-party hosted page
- Prune docs platform members to the editors you actually need, require two-factor authentication for all of them, and keep a reviewed change log
- Monitor addresses and outbound links in your docs for changes and alert a person when anything moves
The unauthorized access at GitBook, the impact on multiple customers, the services taken offline and the ongoing data review come from GitBook's official incident notice. The unauthorized activity on trade[XYZ]'s docs and its warning not to click links come from press reports. PancakeSwap's takedown and migration come from its official X account. What exactly was changed, how access was gained and which customers were affected have not been disclosed, and this article does not speculate. This article does not cover attack details.
Sources
- GitBook official incident notice (2026-11-03) ↗
- GitBook on X (2026-11-03) ↗
- PancakeSwap on X: aware of the GitBook incident, docs taken offline as a precaution (2026-11-03) ↗
- crypto.news: Trade.xyz restores GitBook docs, warns users against links ↗
- The Crypto Times: trade.xyz Reports Unauthorized Activity on GitBook Documentation ↗
Also on X · Nov 3, 2026: View the original post on X ↗