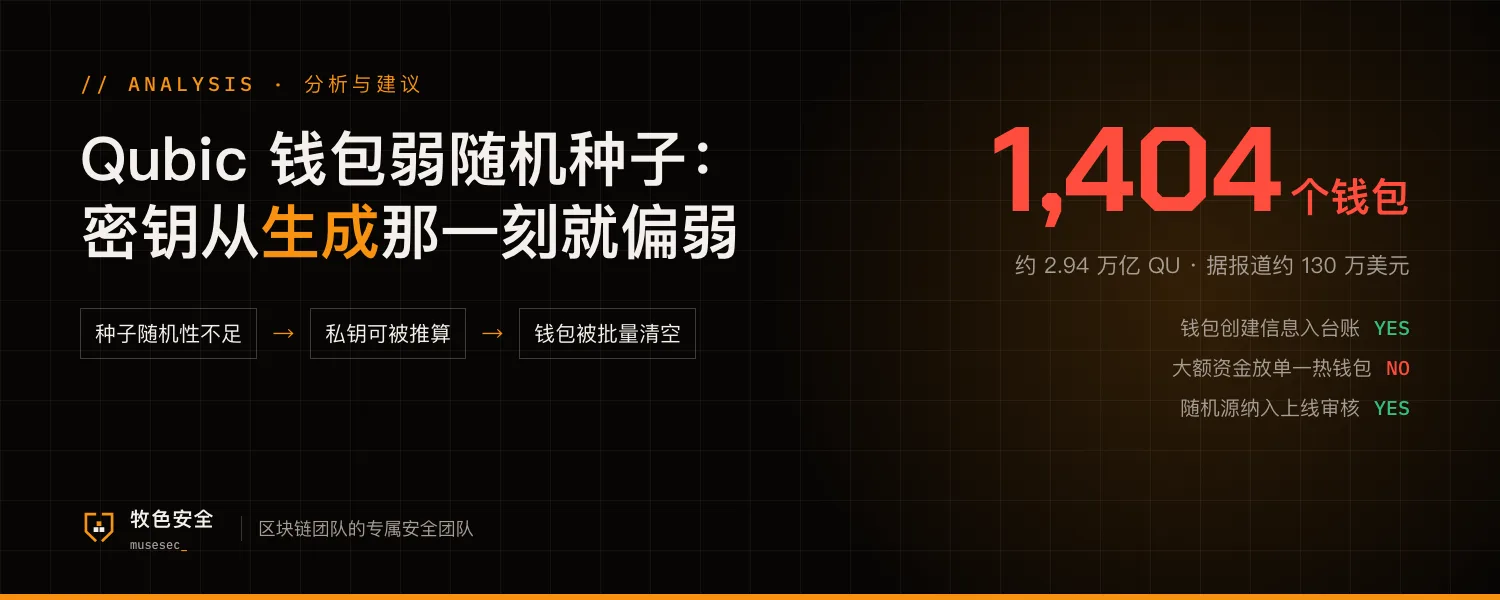
According to Qubic, between 23:42 UTC on October 17 and 01:26 UTC on October 18 an attacker drained 1,404 wallets holding about 2.94 trillion QU, reported to be worth around $1.3 million. Qubic says some wallet seeds were generated with insufficient randomness, and that the problem lay in seed generation rather than in the protocol itself.
SlowMist (@SlowMist_Team) found that the wallet relied on Math.random(), a source of randomness that is not cryptographically secure. Qubic says about 87.1% of the stolen funds remain frozen on-chain and that version 4.26.4 fixes the issue.
Where small teams are exposed
Process
Wallets and signing tools are usually chosen by reputation. Few teams check whether a tool has been externally audited, where keys are generated, or how users will be told when something goes wrong.
Risk
A key that is weak from the moment it is created cannot be saved by good backups, multisig or access controls later on. And because exposure depends on when, on which device and with which version a wallet was created, it is hard to check after the fact.
Privileges
If a team keeps its funds in a single hot wallet created with an old version, one seed flaw is enough to lose all of it.
Five things you can do now
- Inventory every wallet the team uses, recording the tool, device and version it was created with, in your asset register
- Subscribe to security notices from your wallet and tool vendors, and if you are affected, follow your playbook to generate new addresses in a clean environment and move assets promptly
- Keep large balances in hardware wallets or multisig, with hot wallets holding only day-to-day working funds
- In your own products, check that all code generating keys, seed phrases or random tokens uses a cryptographically secure source of randomness, and make this part of pre-release review
- Set up a process for receiving and following up on vulnerability reports. BlockSec Phalcon says this issue was reported as early as February and was not properly addressed at the time
The US dollar figure is a media estimate (about $1.3 to 1.4 million). Wallet count, QU amount, frozen share and fix version follow Qubic's official statement.
Sources
- Qubic: official security incident update (2026-10-18) ↗
- SlowMist: Qubic wallet vulnerability analysis (2026-10-20) ↗
- BlockSec Phalcon: the issue had been reported earlier (2026-10-19) ↗
- The Crypto Times: Qubic Halts Network After $1.3M Drain Hits 1,404 Wallets Through Weak Seeds ↗
Also on X · Oct 20, 2026: View the original post on X ↗