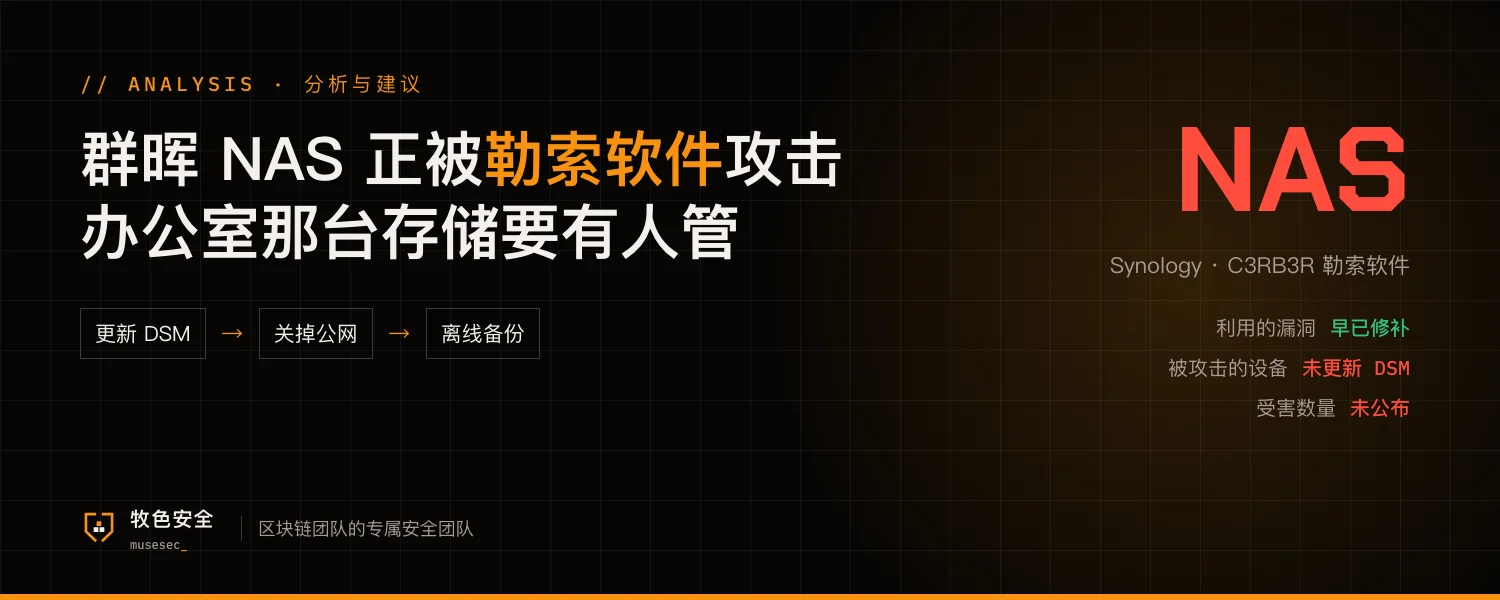
Synology said on October 29 that attackers are exploiting a vulnerability patched in December 2024 to target NAS devices running outdated DSM versions, encrypting data and demanding ransom. The company is urging everyone on an affected version to update DSM immediately and turn on automatic updates. According to public reports, the ransomware in this campaign is called C3RB3R and encrypted files get a .L0CK3D extension.
According to security researchers, some incidents also involve newer flaws disclosed in September, so the exact entry point is still disputed, and Synology has not published a victim count. Over the past few days, small companies have reported having all their files encrypted because the office NAS had gone unpatched for a long time.
Where small teams are exposed
Process
A NAS gets set up once and then forgotten. Updates, account cleanup and backup checks are nobody's job, and the last update turns out to be two years old only after something goes wrong.
Risk
Many teams expose the NAS directly to the internet so people can reach it from home or on the road. Unpatched and exposed, it will be found by mass scanning sooner or later, and if the only backup lives on the same box, encryption leaves you nothing to restore from.
Privileges
A NAS often holds contracts, finance sheets, server configs and sometimes wallet backups or key files. Losing one device can mean losing more than documents. It can mean losing whatever moves money.
Five things you can do now
- Log in to your NAS today, check the DSM version, update to the latest release and enable automatic security updates
- Close any port forwarding to the NAS and move remote access behind a VPN or zero-trust access
- Keep at least one backup that does not live on this NAS (an offline drive or separate storage), enable immutable snapshots, and test a restore
- Keep seed phrases, private keys and keystore files off the NAS and off every shared drive
- Clean up NAS accounts, disable the default admin account and require two-factor authentication for everyone
That attacks target outdated DSM through a vulnerability patched in December 2024, and the update guidance, come from Synology's official statement. The ransomware name and file extension come from public reports. The claim that some incidents involve flaws disclosed in September 2026 comes from security researchers. The victim count and the entry point for each incident have not been published. This article does not cover attack details.
Sources
- Synology statement: C3RB3R ransomware (2026-10-29) ↗
- The Hacker News: Synology NAS Devices Targeted in Ransomware Attacks Exploiting Patched DSM Flaw ↗
- BleepingComputer: Synology warns of C3RB3R ransomware attacks targeting NAS devices ↗
- Gridinsoft: Synology NAS Ransomware Locks Files as Sources Disagree on Entry ↗
Also on X · Nov 3, 2026: View the original post on X ↗