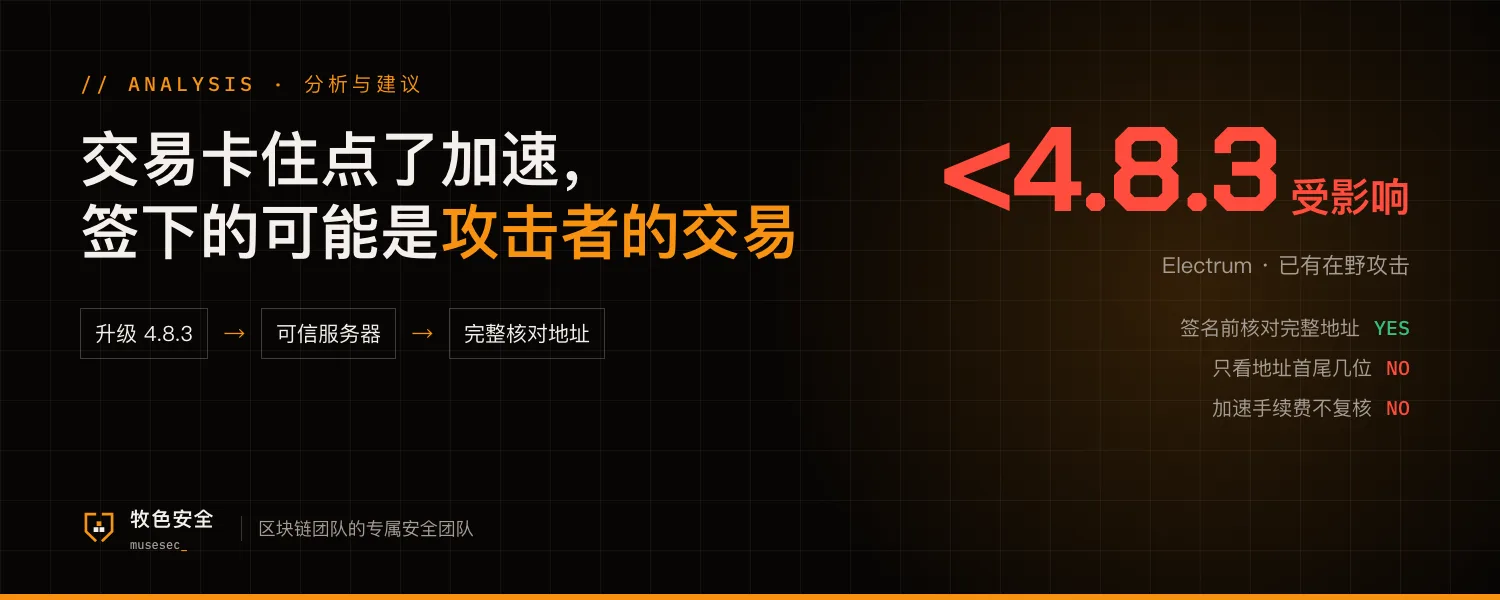
On October 24, Bitcoin wallet Electrum published a high-severity advisory. Versions before 4.8.3 display unconfirmed transactions from the connected server without verifying their signatures. A malicious server can swap a just-broadcast payment for one with a different destination address, and if the user then bumps the fee (RBF), they sign a valid transaction that pays the attacker.
Electrum confirmed attacks in the wild, with attacker addresses matching the last four characters of the legitimate address. According to reports, developers received two user reports, at least one user lost funds, and the total has not been disclosed. Version 4.8.3 fixes the issue by verifying signatures on unconfirmed transactions that spend the wallet's own coins. Users connected to their own or trusted servers are not exposed to this attack.
Where small teams are exposed
Process
Many teams use Electrum for BTC reserves and routine payments, and "bump it if it's stuck" is standard practice. Few treat a fee bump as a new signature that needs review.
Risk
The wallet connects to public servers by default and shows whatever the server returns. Checking only the first and last few characters of an address is exactly the habit this attack exploits.
Privileges
When one person can both initiate a payment and bump the fee alone, with no second check, a single mistaken signature moves funds.
Five things you can do now
- Upgrade every Electrum install to 4.8.3, downloaded only from the official site with the signature verified
- Point reserve wallets at a server your team runs or explicitly trusts, not the default public server list
- Treat every fee bump or replacement as a new transaction. Check the full destination address and amount before signing, not just the first and last few characters
- Hold larger BTC balances in multisig or on hardware wallets, verify the full address on the device screen, and split initiating and signing between different people
- Review fee bumps from the past month and confirm the address that finally landed on chain matches the original payment
The sequence of events follows Electrum's official security advisory; the total loss has not been disclosed. This article does not cover attack details.