On October 21, cloud deployment platform Railway disclosed unauthorized access to the systems that store customer environment variables. Some encrypted variables were decrypted, and these can include API keys and database and registry credentials. Railway paused all deployments and advised every user to rotate the variables and private registry credentials stored on the platform and to review the logs of affected services.
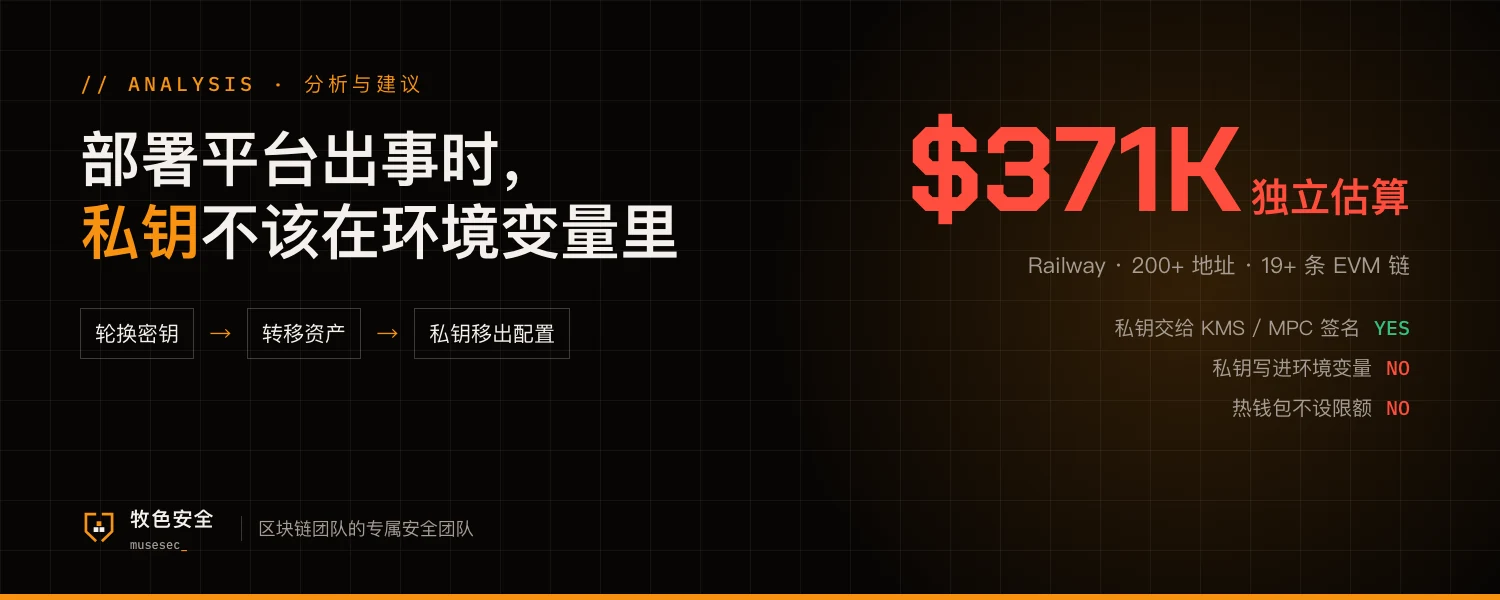
According to security researchers, starting at 19:36 UTC that day a sweeper script moved funds out of more than 200 addresses across 19+ EVM chains, with losses independently estimated at about $371K. The drained keys are suspected to have come from the exposed environment variables. Railway has not confirmed the link between these losses and the incident.
Where small teams are exposed
Process
To ship fast, wallet private keys and seed phrases often go into platform environment variables like any other config, with no line drawn between ordinary settings and keys that can move money.
Risk
When the platform itself is breached, every customer's secrets are exposed at once. Attackers sweep them with off-the-shelf scripts, and on-chain transfers complete within minutes, well before anyone can rotate.
Privileges
A single hot wallet key usually carries full control of that wallet, with no limits and no second approver. Once it leaks, the wallet is gone.
Five things you can do now
- Today, list every service you run on Railway or similar hosted platforms, rotate every secret in their environment variables, and move funds out of any wallet whose key was stored there
- Review the last 48 hours of access logs for those services, plus your cloud account and third-party API activity, for anything unusual
- Stop putting private keys and seed phrases in environment variables. Use KMS, HSM or an MPC signing service so the application can request signatures without ever holding the key
- Keep only a day's working balance in hot wallets, set per-transaction and daily limits, and route large withdrawals through multisig
- Put on-chain monitoring on every hot wallet address and alert on any unexpected outflow
Scope and required actions follow Railway's official disclosure; the loss figure is an independent estimate by security researchers. This article does not cover attack details.