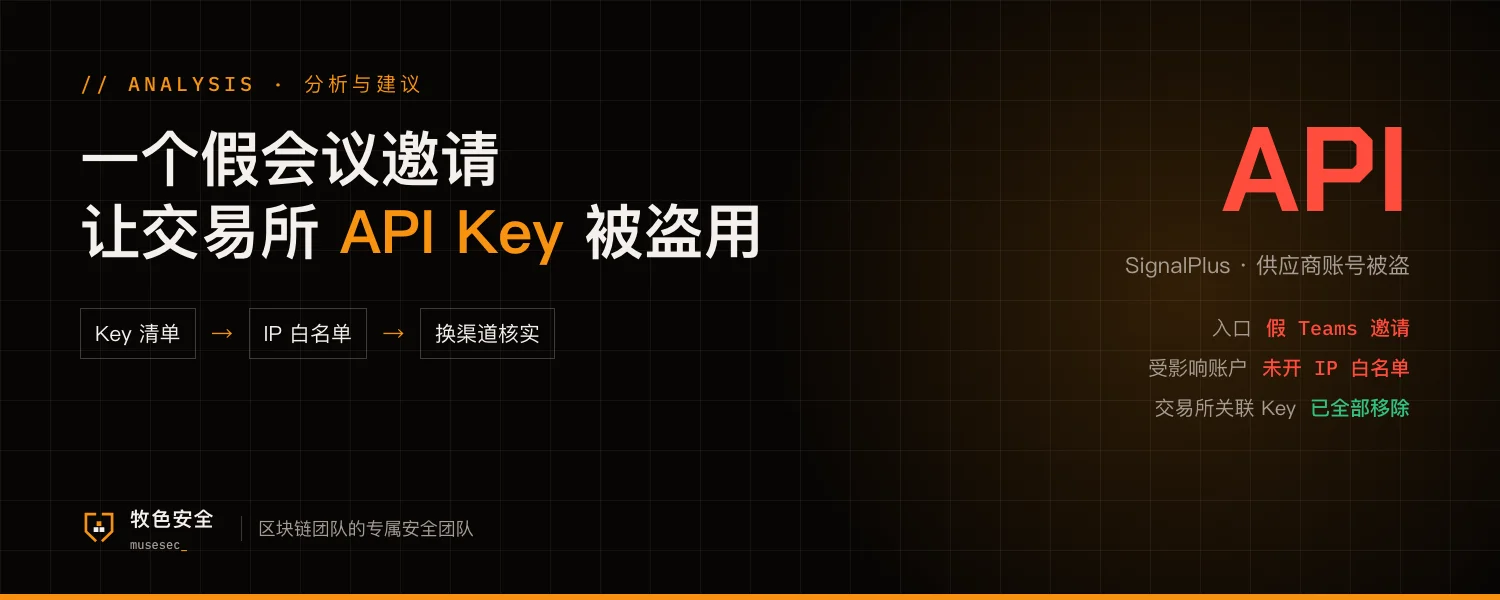
Options trading terminal SignalPlus was attacked in the early hours of November 4. According to the company, the attack began with a compromised third-party Telegram account and affected a small number of accounts without IP whitelisting. Total losses are under $82,000 and affected users will be reimbursed in full. The terminal has been paused, and SignalPlus worked with exchanges to revoke all API keys linked to it.
Per its incident statement and media reports, the attacker took over the Telegram account of a contact at a technology vendor, used it to send an engineer a fake Teams meeting invite, compromised the engineer's computer, and then used that access to reach internal systems. SignalPlus acknowledged it had not required clients to bind exchange API keys to an IP whitelist. Binance and Deribit have since removed all SignalPlus-linked API keys, and both say their own systems were not affected.
Where small teams are exposed
Process
A meeting link from someone you know rarely gets a second check. Once that person's account is taken over, the existing relationship becomes the perfect cover.
Risk
Many trading teams hand exchange API keys to third-party terminals, bots or data tools. Those keys can place and cancel orders, and some can move funds. If one machine inside the tool provider is compromised, your account can be used without you noticing right away.
Privileges
An API key with no IP whitelist works from anywhere. Few teams can say exactly which keys they have handed out, what each one can do, when it expires and where it is used.
Five things you can do now
- Build an inventory: every API key on every exchange, which third-party tool holds it, and what permissions it has
- Bind every API key to an IP whitelist, turn off withdrawal and transfer rights you do not need, and delete keys that are no longer used
- Give each third-party tool its own sub-account funded only with what that tool needs
- Confirm meeting invites and install links through a second channel, such as a phone call or a different messenger, even when they come from people you know. Do not install meeting clients from unfamiliar links
- If you are the tool provider: require clients to whitelist IPs, keep engineers' laptops separate from systems that store client keys, and require approval and logging for access
The scope, loss figure, reimbursement and API key revocation come from SignalPlus's official statement. The fake Teams invite and the compromised vendor Telegram account come from its incident statement and media reports. Binance and Deribit removing linked API keys comes from their announcements and media reports. This article does not cover attack details.
Sources
- SignalPlus official statement (X, 2026-11-05) ↗
- CoinDesk: Binance cuts SignalPlus access after security warning, urges users to check accounts ↗
- crypto.news: SignalPlus hack, Binance and Deribit revoke API keys ↗
- bizinsider: Binance, Deribit revoke SignalPlus API keys after fake Teams invite attack ↗
Also on X · Nov 6, 2026: View the original post on X ↗