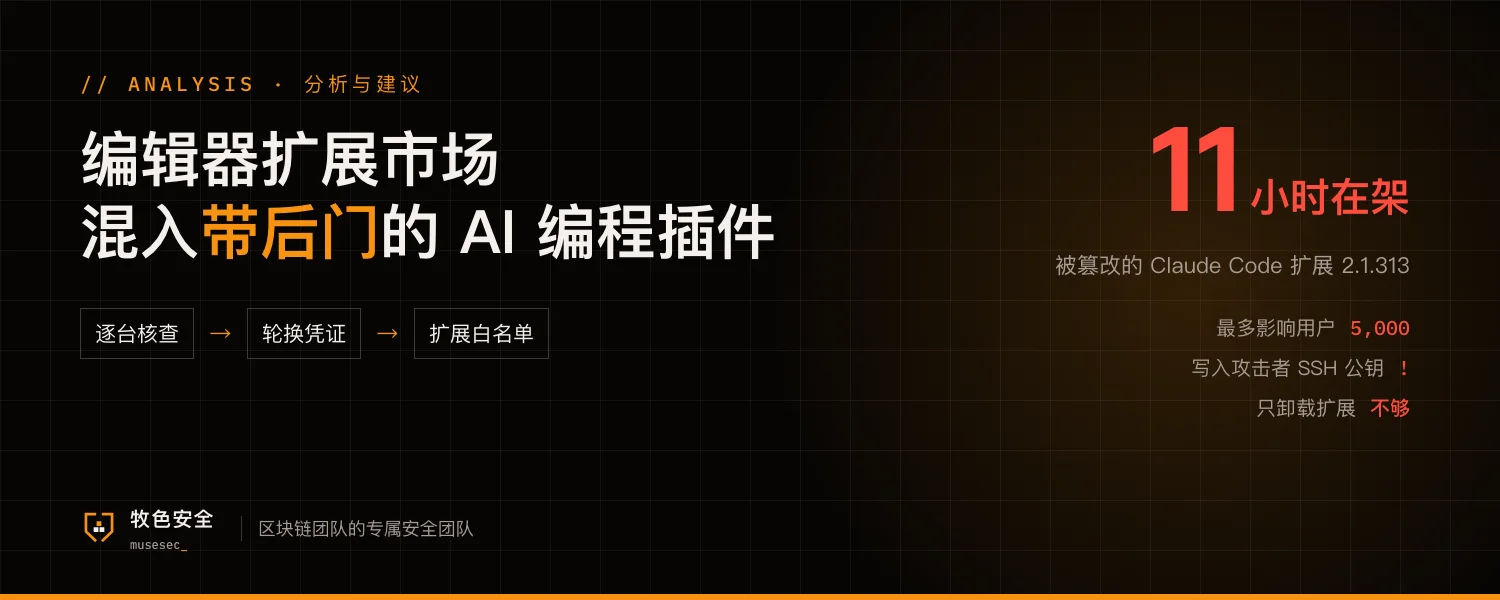
On October 29, a tampered version of the Claude Code extension (v2.1.313) was listed on the extension marketplace of the AI editor Cursor for about 11 hours. Up to 5,000 users installed it or auto-updated to it. Cursor says this version was not developed by Anthropic. Once installed, it collected the hostname, username, Git email and public IP, added an attacker's key to the machine's SSH authorized keys, installed a startup script and tried to open a reverse SSH tunnel.
Cursor removed the version, took its whole marketplace offline for a period, rotated keys and worked with the hosting provider to take down the attacker's server. It warns that uninstalling the extension is not enough, because the startup script keeps running, and affected users need to follow the cleanup steps and rotate credentials. Cursor has not said how the malicious version got into the marketplace.
Where small teams are exposed
Process
Editor extensions are usually installed by developers themselves and auto-update by default, with no approval and no record of who runs what. When a trusted plugin ships a malicious update, nobody on the team notices.
Risk
Developer machines hold SSH keys, cloud accounts, repository tokens, deployment scripts and sometimes test or operations wallets. The preliminary cause Binance shared the same week was also one operations engineer's compromised laptop. Developer and DevOps machines are often where an attack starts.
Privileges
A backdoor on one developer machine gives the attacker every system that person can reach. The more access developers hold on servers, CI and cloud, the wider the blast radius.
Five things you can do now
- Ask the team who uses Cursor and whether anyone installed or updated the Claude Code extension on October 29, then check each machine using the steps in Cursor's official notice
- Isolate any affected machine from the network, clean it following the official steps and consider a full rebuild. From a separate clean device, rotate the SSH keys, cloud credentials, Git tokens and API keys that machine could reach
- Turn off auto-updates for editor extensions on developer machines, pin versions of critical plugins, and wait a day or two before upgrading
- Keep an approved list of editor extensions and AI coding tools, manage them as vendors, and do not install anything outside the list
- Keep production keys, signing and deployment rights off everyday developer machines. Put them on dedicated devices behind multi-person approval
The exposure window, number of affected users, extension behavior and response steps come from Cursor's official security notice. Cursor has not disclosed how the malicious version entered the marketplace, and this article does not speculate. This article does not cover attack details.
Sources
- Cursor security notice: malicious version of Anthropic.claude-code (2.1.313) identified in the Cursor Extension Marketplace ↗
- Cursor on X (2026-10-30) ↗
- Unite.AI: Cursor Discloses SSH Backdoor Attempt in Malicious Claude Code Extension ↗
- GBHackers: Malicious Claude Code VS Code Extension Installs Persistent SSH Backdoor ↗
Also on X · Oct 31, 2026: View the original post on X ↗