RESEARCH

Security Research

We review public security incidents and turn them into defenses blockchain teams can put in place right away. Defense only, no attack walkthroughs.

RSS feed ↗
A compliance vendor was breached, and the first notice understated it

Analysis

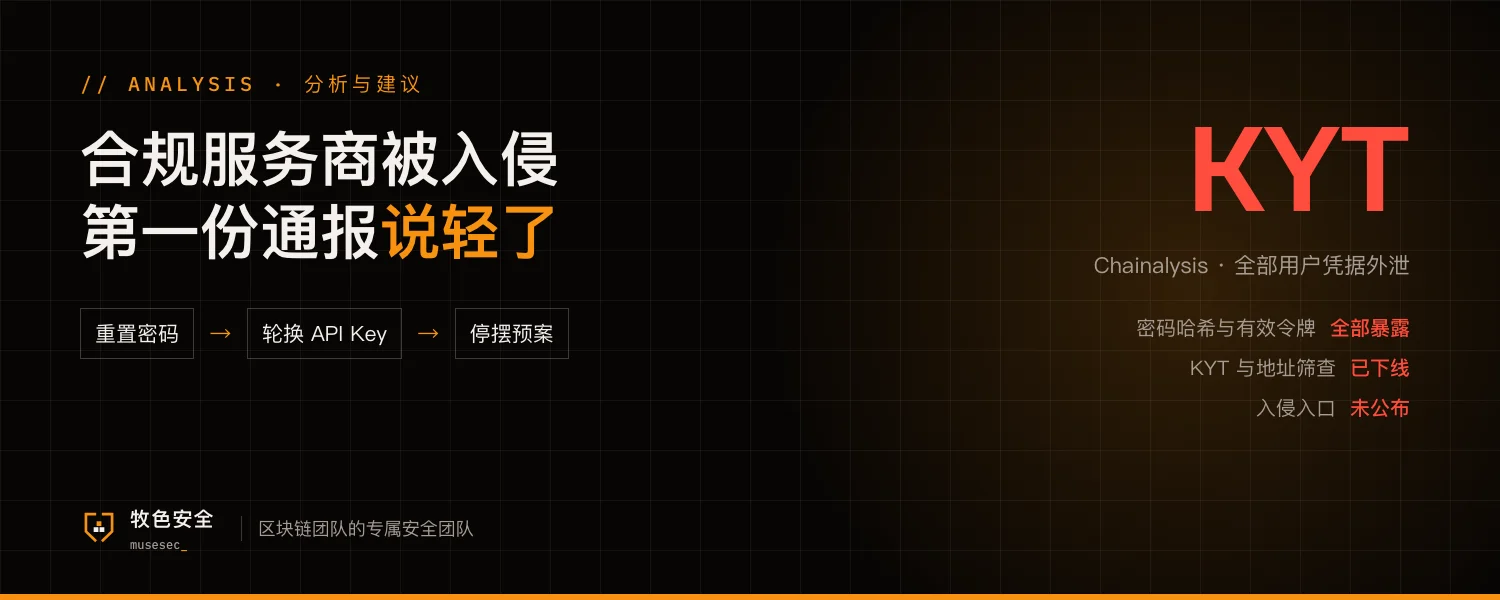
A Compliance Vendor Was Breached, and the First Notice Understated It: Chainalysis Exposes All User Credentials

Chainalysis disclosed a breach on October 30. A November 4 update confirmed that password hashes and live tokens for all users were exposed, and KYT and address screening were taken offline. What dependence on compliance and risk vendors means for a blockchain team of 10 to 50 people, viewed through process, risk and privileges, with five steps to take now.

#Compliance#Supply chain

Read article →
Synology NAS devices are being hit by ransomware

Analysis

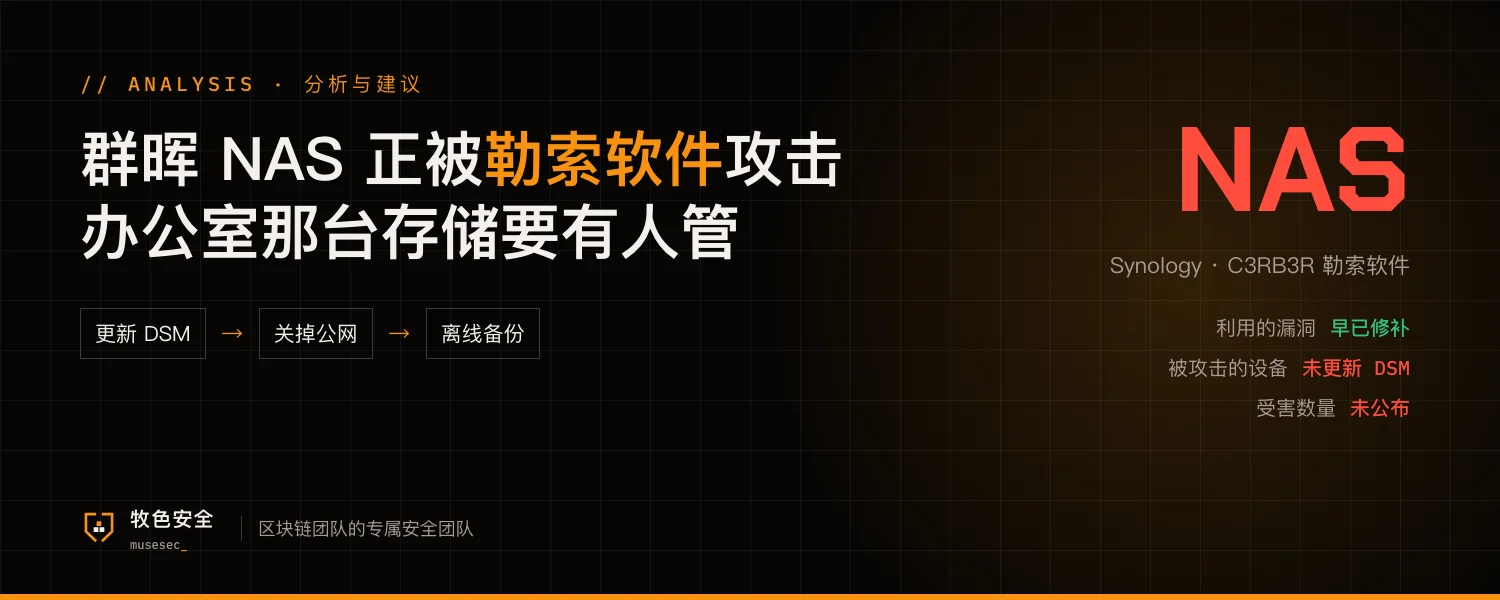
Synology NAS Devices Are Being Hit by Ransomware: The Storage Box in Your Office Needs an Owner Too

On October 29, Synology warned that attackers are exploiting a vulnerability patched in late 2024 to target NAS devices on outdated DSM, encrypting data and demanding ransom. What this means for the office NAS at a blockchain team of 10 to 50 people, viewed through process, risk and privileges, with five steps to take now.

#Servers & infrastructure#Endpoint & mobile

Read article →
A docs hosting platform had a security incident

Analysis

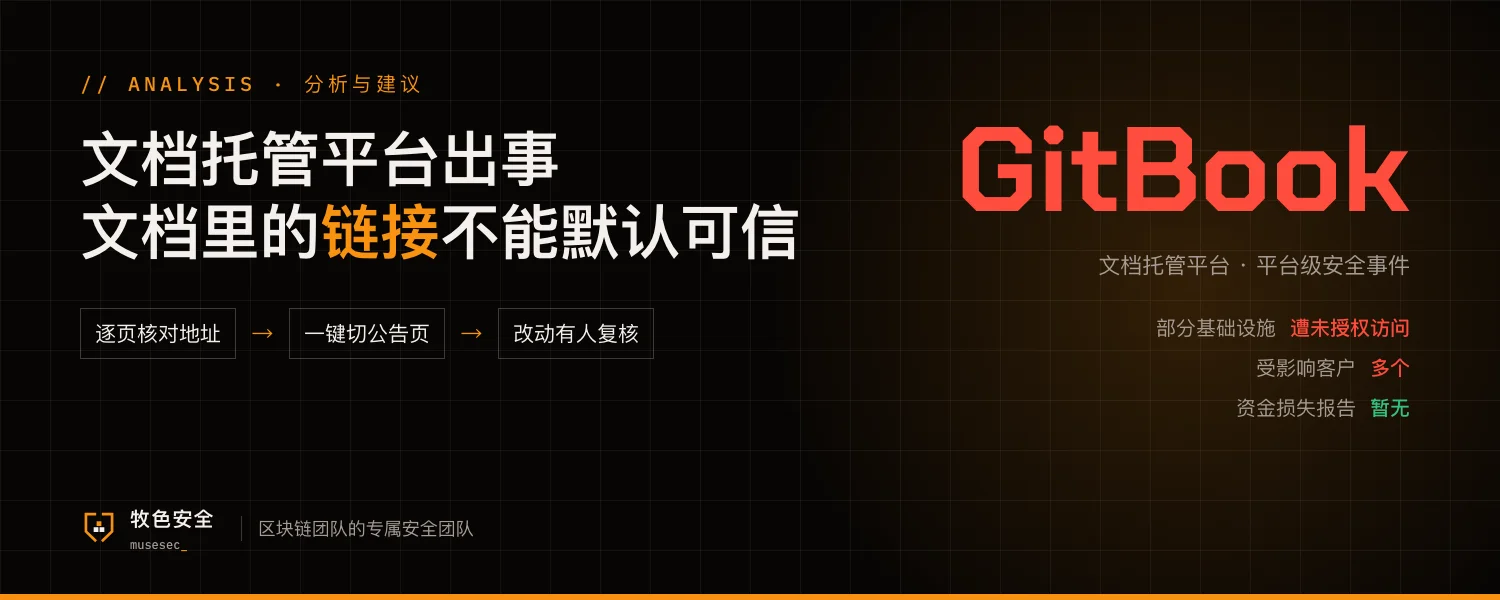
A Docs Hosting Platform Had a Security Incident: Links in Your Docs Should Not Be Trusted by Default

On November 2, docs hosting platform GitBook detected unauthorized access to parts of its infrastructure, affecting a number of customers. A perpetual futures platform reported unauthorized activity on its docs, and a DEX moved its docs off GitBook. How blockchain teams of 10 to 50 people should manage third-party hosted docs, viewed through process, risk and privileges, with five steps to take now.

#Supply chain#Phishing & social engineering

Read article →
Hot wallets on a dozen-plus chains drained within half an hour

Analysis

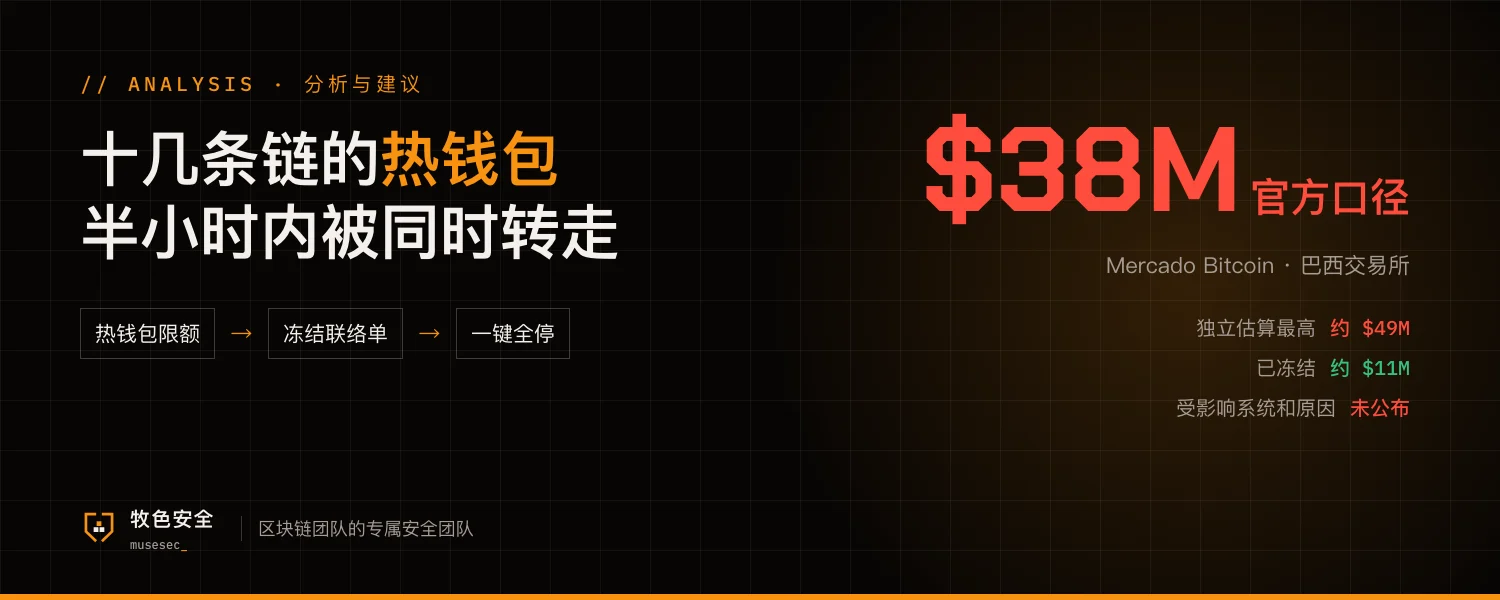
Hot Wallets on a Dozen-Plus Chains Drained Within Half an Hour: What the Mercado Bitcoin Incident Means for Small Teams

On November 2, Brazilian exchange Mercado Bitcoin detected a security incident and suspended all transactions. The exchange says about $38M is involved and about $11M has been frozen. Funds left more than a dozen chains, and according to researchers most transfers happened within roughly 34 minutes. How blockchain teams of 10 to 50 people should manage hot wallets across many chains, viewed through process, risk and privileges, with five steps to take now.

#Exchange & funds#Wallets & signing

Read article →
Hot wallets on self-hosted payment servers are being swept

Analysis

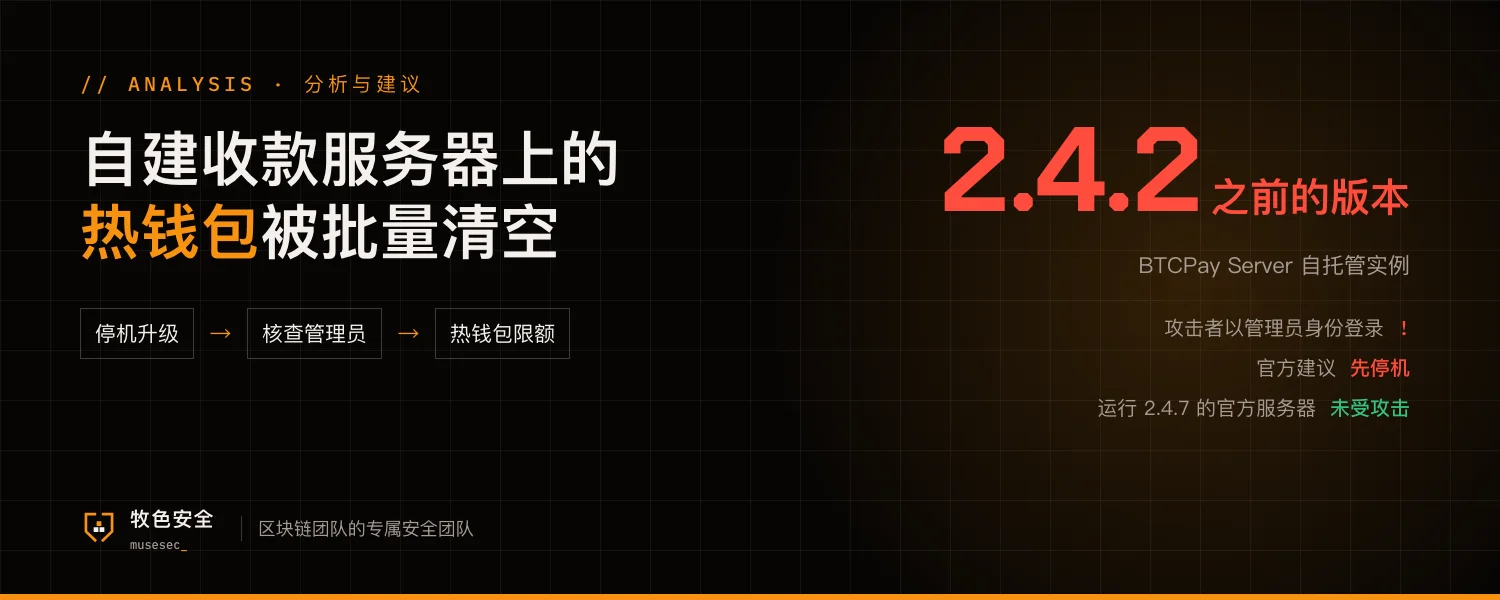
Hot Wallets on Self-Hosted Payment Servers Are Being Swept: What the BTCPay Incident Means for Small Teams

On November 1, BTCPay Server warned that hot wallets on multiple self-hosted instances were being swept and asked operators to shut down. Reports involve versions older than 2.4.2, where the attacker logged in as an administrator. How blockchain teams of 10 to 50 people should run payment servers and hot wallets, viewed through process, risk and privileges, with five steps to take now.

#Wallets & signing#Servers & infrastructure

Read article →
One registrar incident turned a dozen DeFi websites into wallet drainers

Analysis

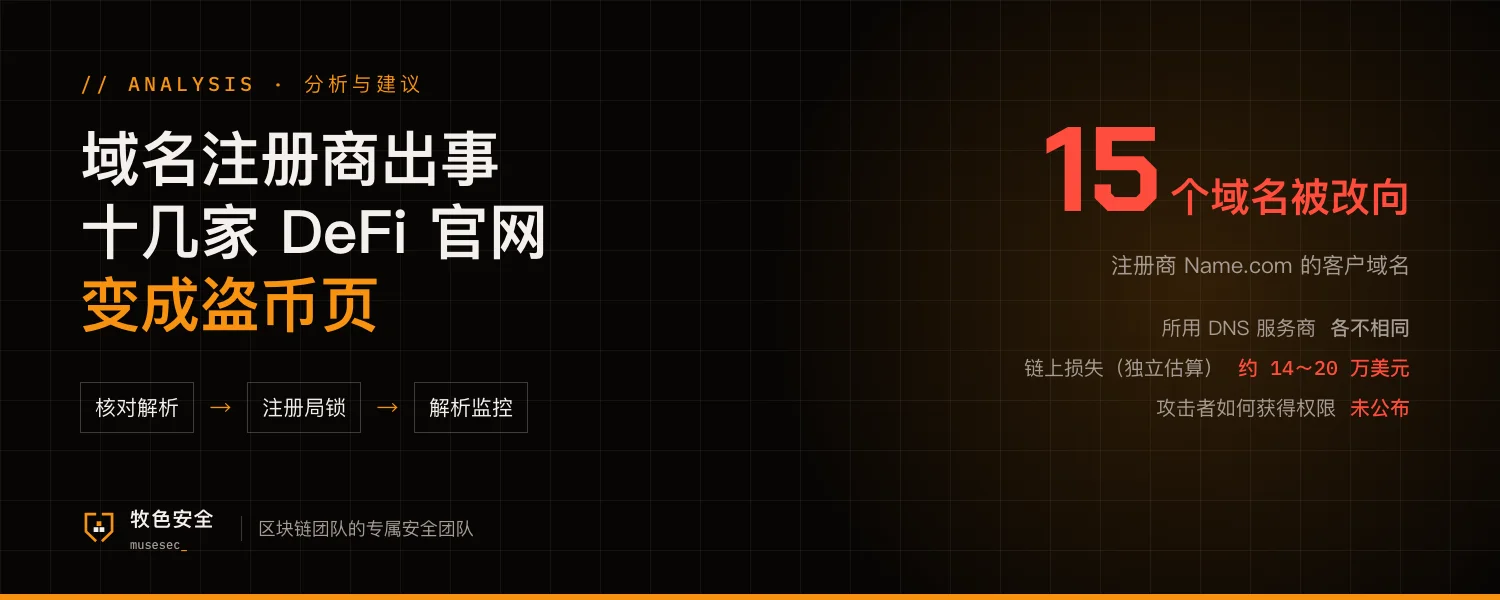
One Registrar Incident Turned a Dozen DeFi Websites Into Wallet Drainers: Your Domain Is the First Door

Starting October 30, 15 customer domains registered with Name.com were redirected without authorization, sending visitors of DeFi sites such as Flap and Kintsu to pages serving a wallet drainer. Independent estimates put losses at roughly $140K to $200K. How blockchain teams of 10 to 50 people should protect domains, DNS and registrar accounts, viewed through process, risk and privileges, with five steps to take now.

#Phishing & social engineering#Servers & infrastructure

Read article →
A backdoored AI coding extension slipped into an editor marketplace

Analysis

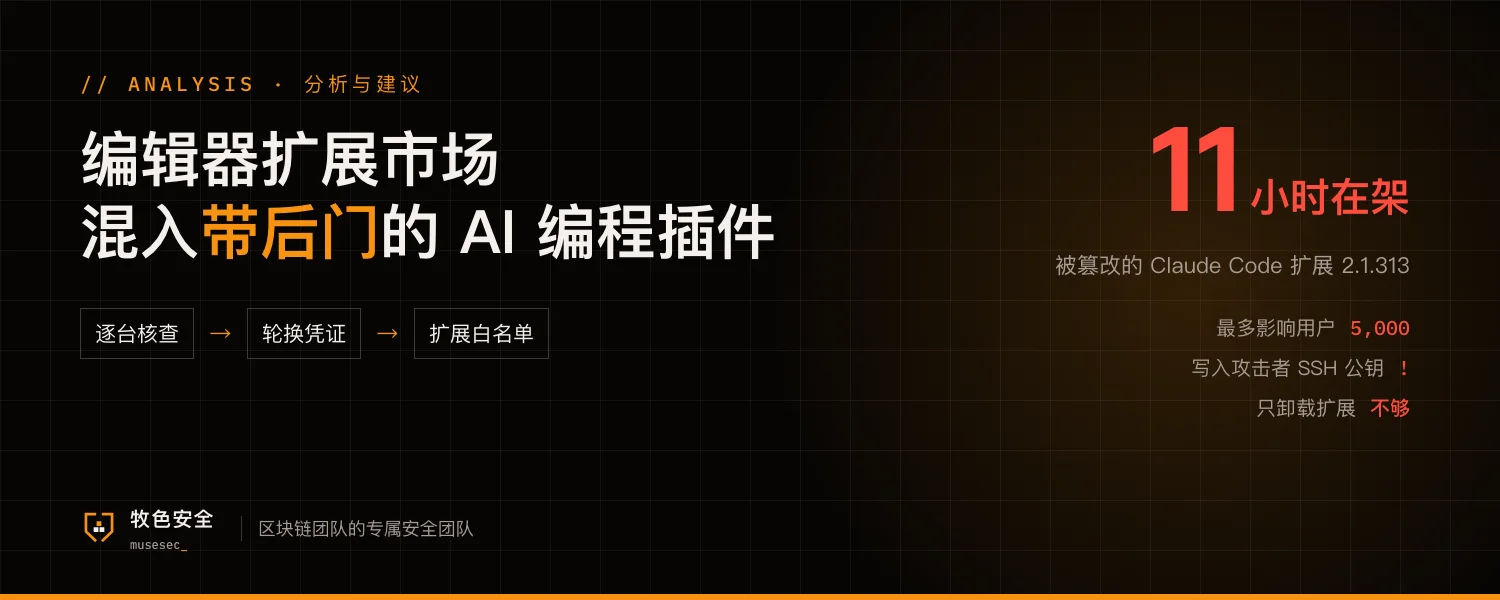
A Backdoored AI Coding Extension Slipped Into an Editor Marketplace: Why Developer Machines Are the First Door

On October 29, a tampered Claude Code extension (v2.1.313) was listed on the Cursor extension marketplace for about 11 hours, reaching up to 5,000 users. It added an attacker's SSH key and installed a persistent startup script. How blockchain teams of 10 to 50 people should manage editor extensions and AI coding tools on developer machines, viewed through process, risk and privileges, with five steps to take now.

#Supply chain#Endpoint & mobile

Read article →
Two exchanges in three weeks, likely the same group

Analysis

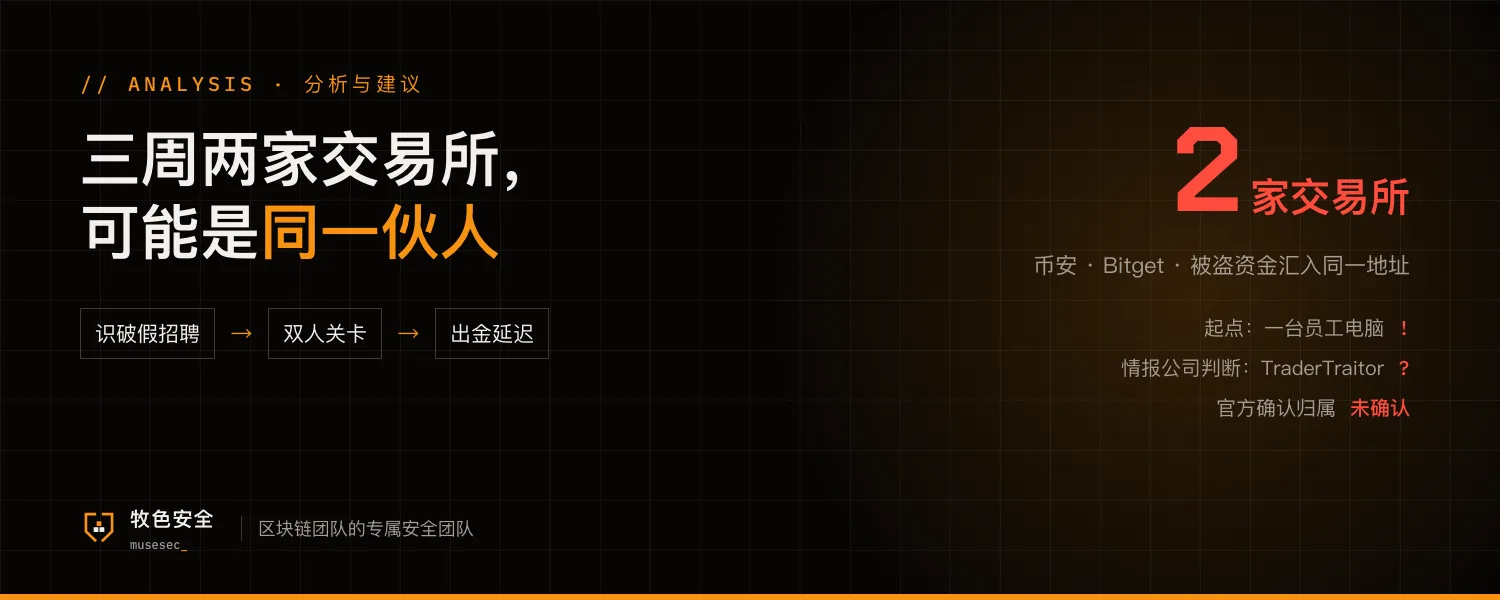
Two Exchange Hacks in Three Weeks, Likely the Same Group: It Started With One Employee's Laptop

On October 30, researchers found funds stolen from Binance and from this month's Bitget hack moving into the same address, and TRM Labs and Chainalysis assess both as the work of North Korea-linked TraderTraitor. Binance added that a compromised employee laptop was only the starting point. How blockchain teams of 10 to 50 people can stop attacks that start on an employee laptop, viewed through process, risk and privileges, with five steps to take now.

#Phishing & social engineering#Exchange & funds

Read article →
One DevOps laptop opened the path to withdrawals

Analysis

Binance's Preliminary Cause: One DevOps Laptop Opened the Path to Withdrawals

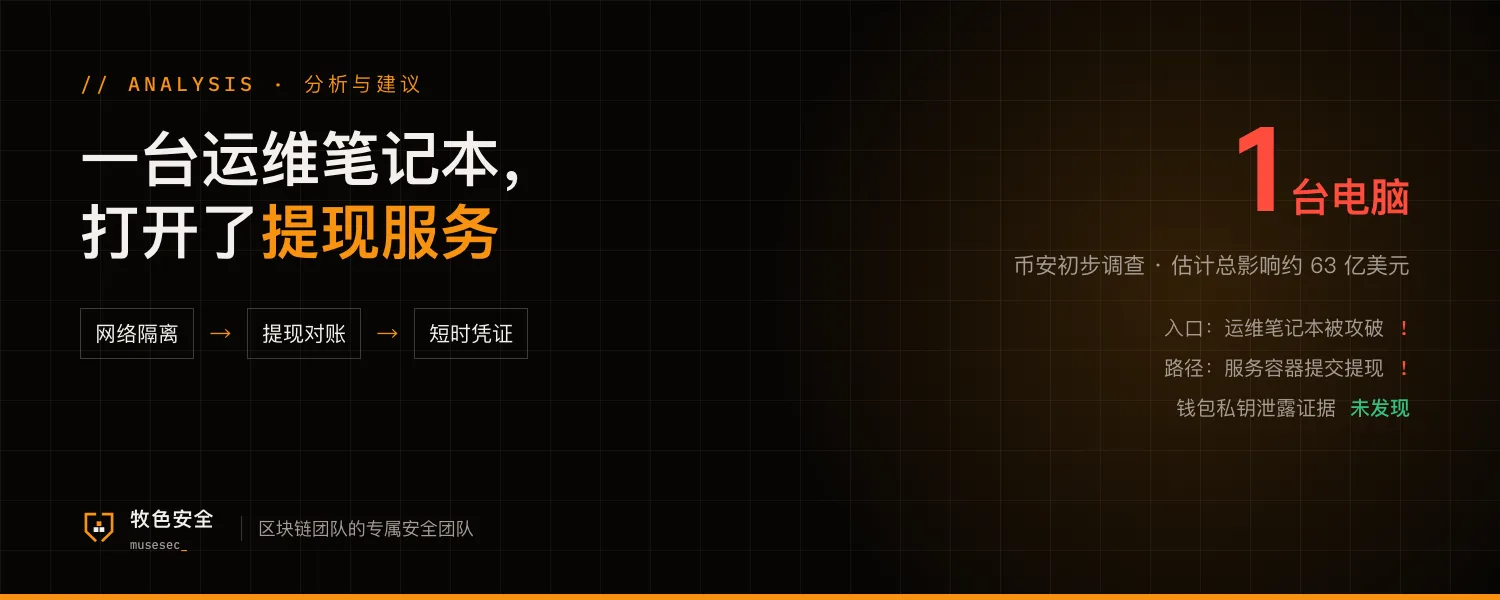
On October 30, Binance said its initial investigation suggests a compromised DevOps engineer's laptop let an attacker reach a service container and submit unauthorized withdrawals, with no evidence of a private key leak and an estimated total impact of about $6.3B. What it means for blockchain teams of 10 to 50 people, viewed through process, risk and privileges, with five steps to take now.

#Endpoint & mobile#Exchange & funds

Read article →
One delegation, one transaction, an empty hot wallet

Analysis

Binance Hot Wallet Swept in One Transaction via EIP-7702 Delegation: Your Signing Policy Needs to Cover This

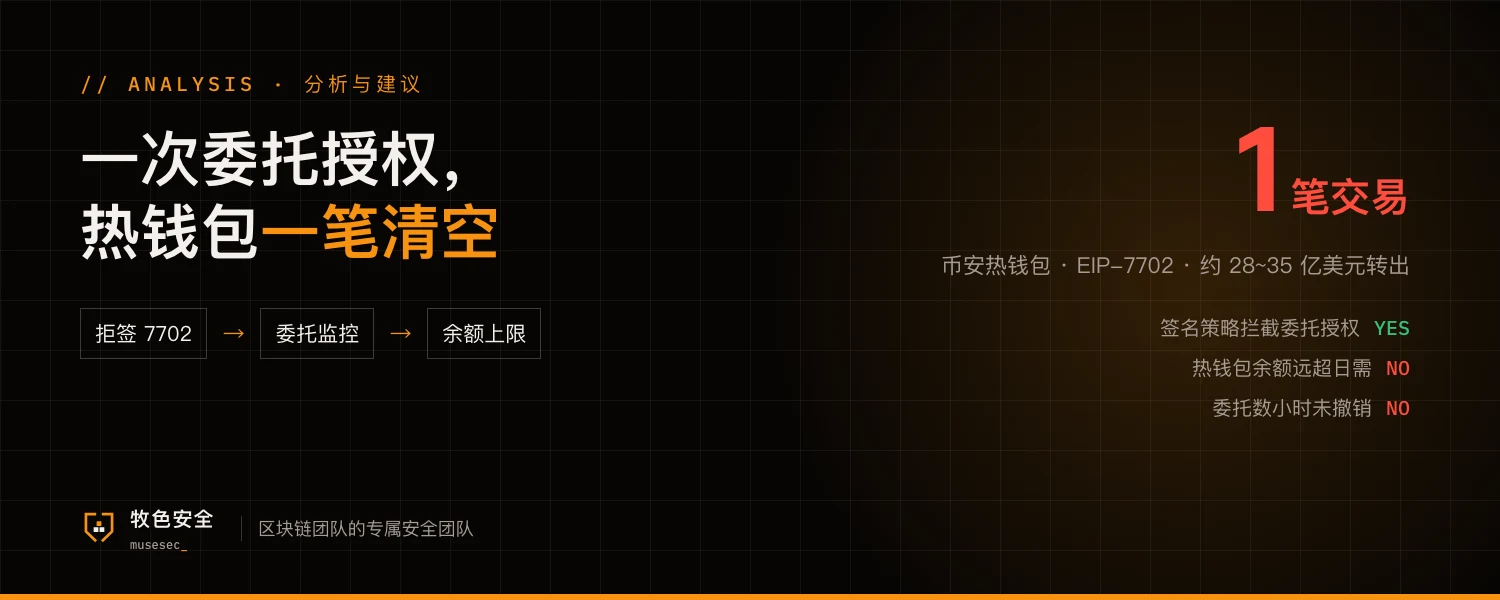
On October 29 (UTC), a Binance hot wallet was given an EIP-7702 delegation and swept of more than 60 assets in one transaction, with outflow estimates of $2.8B to $3.5B. Binance says $2.54B is verified frozen and it will cover all losses. What it means for blockchain teams of 10 to 50 people, viewed through process, risk and privileges, with five steps to take now.

#Wallets & signing#Exchange & funds

Read article →
A page someone else hosts, running on your domain

Analysis

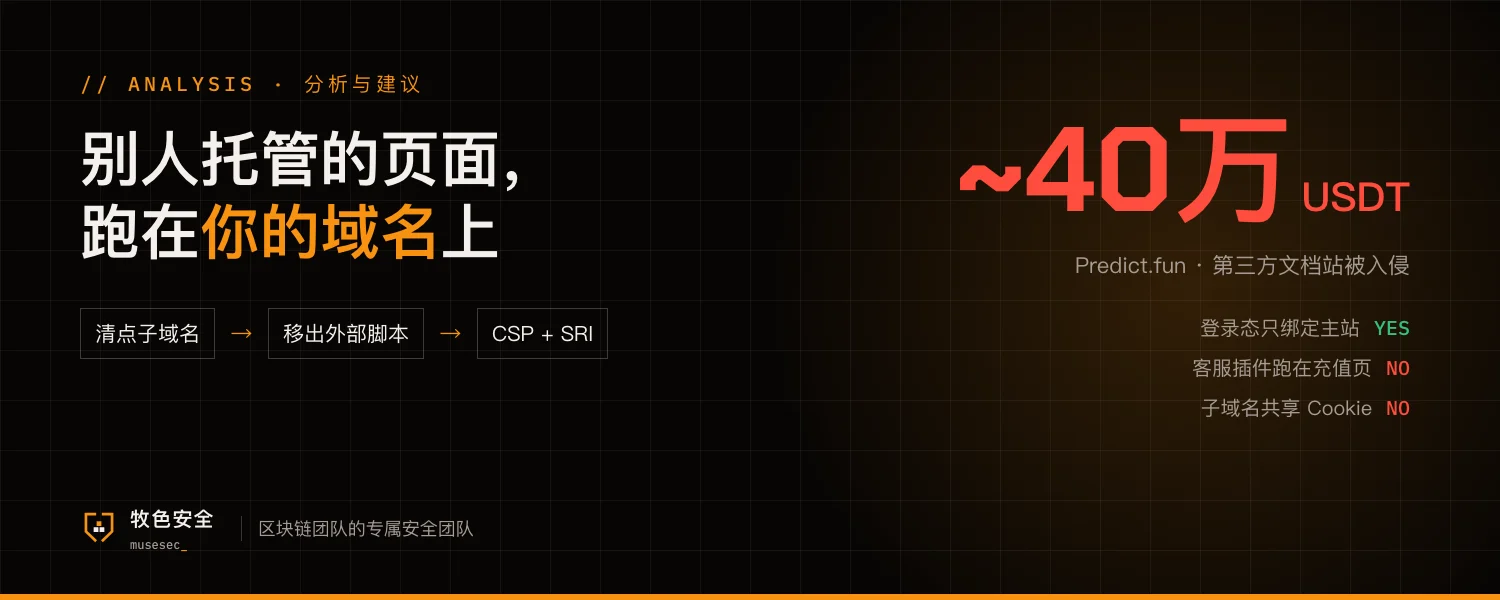
A Third-Party Page on Your Domain Became the Way In: Predict.fun's Docs Site Breach and the Udesk Script Injection

On October 27, prediction market Predict.fun reported about 400,000 USDT in unauthorized transfers, pointing to a compromise of its third-party-hosted API docs site. The same day, security researchers disclosed malicious code in Udesk support scripts that swaps exchange deposit addresses. What it means for blockchain teams of 10 to 50 people, viewed through process, risk and privileges, with five steps to take now.

#Supply chain#Exchange & funds

Read article →
A device that passes the official check may still be counterfeit

Analysis

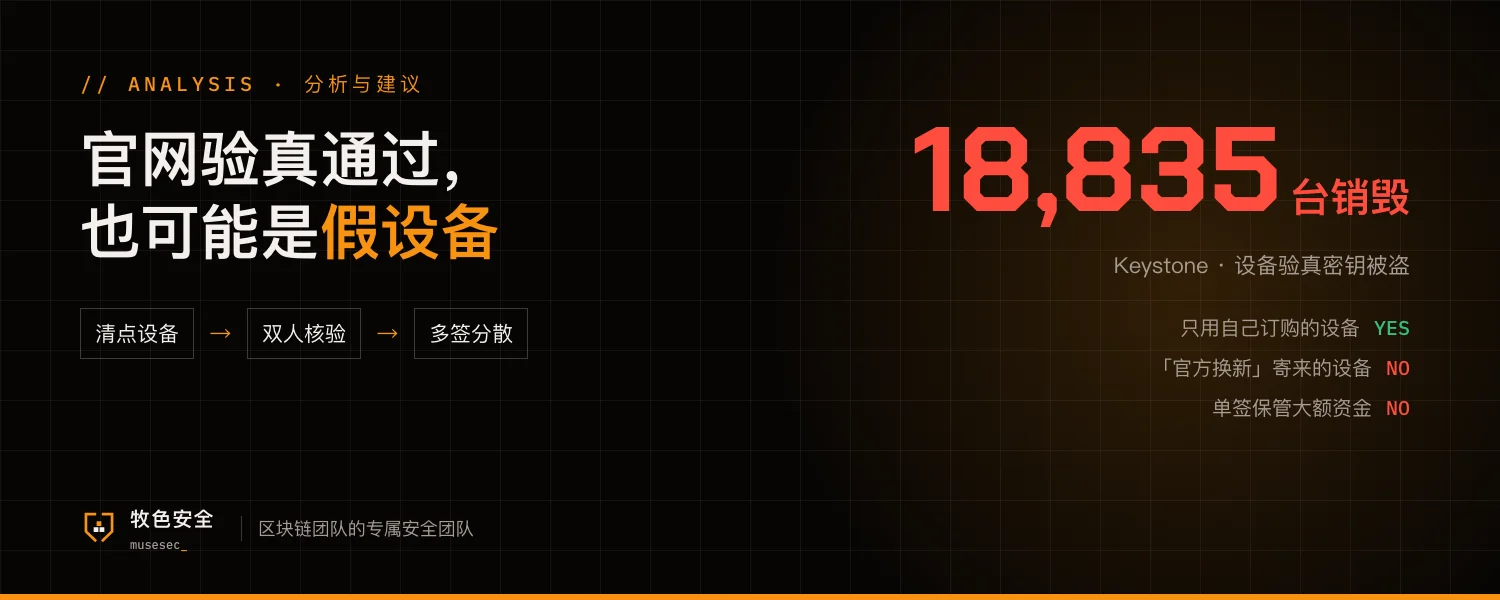
Keystone's Device Authentication Key Was Stolen: Passing the Genuineness Check No Longer Proves a Device Is Real

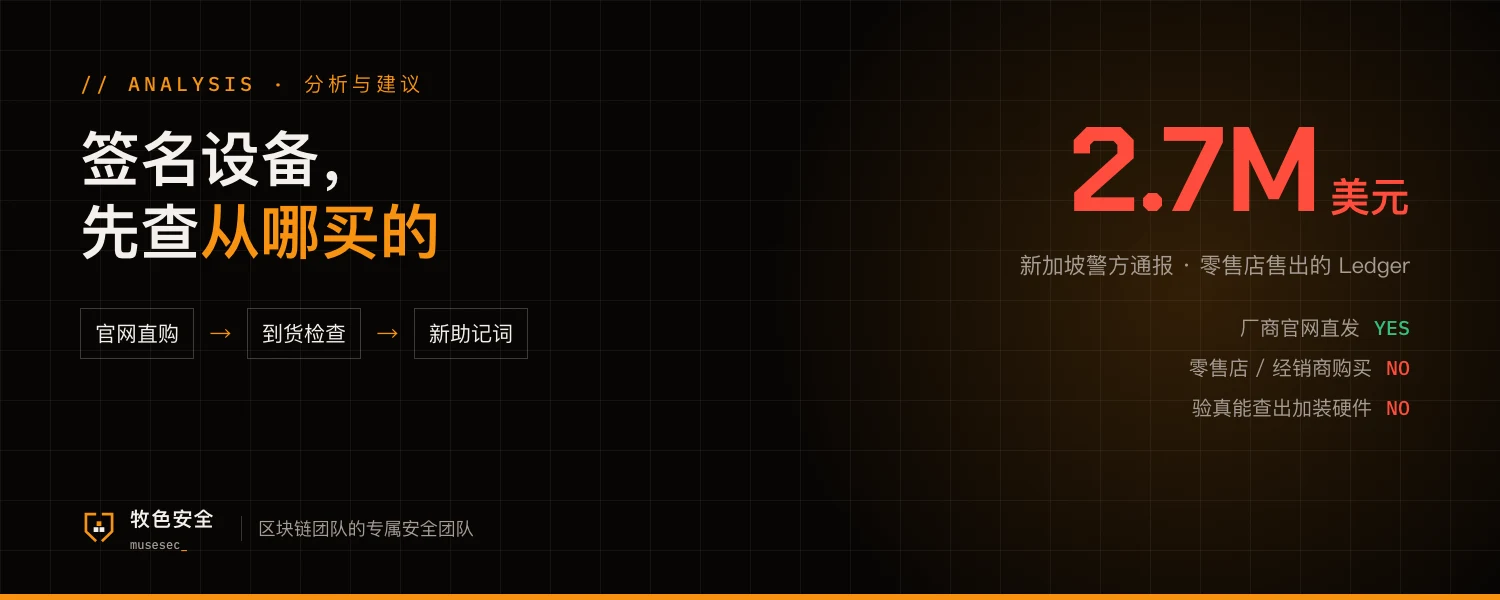
On October 26, hardware wallet maker Keystone published a full statement: an attacker escalated privileges through a vulnerability in a third-party data monitoring tool on its website, taking about 26,000 buyer records and the device authentication key, which allows counterfeits that pass the official check. Keystone will destroy 18,835 inventory units and has paused shipping. What it means for blockchain teams of 10 to 50 people, viewed through process, risk and privileges, with five steps to take now.

#Wallets & signing#Phishing & social engineering

Read article →
The fee bump you sign may pay the attacker

Analysis

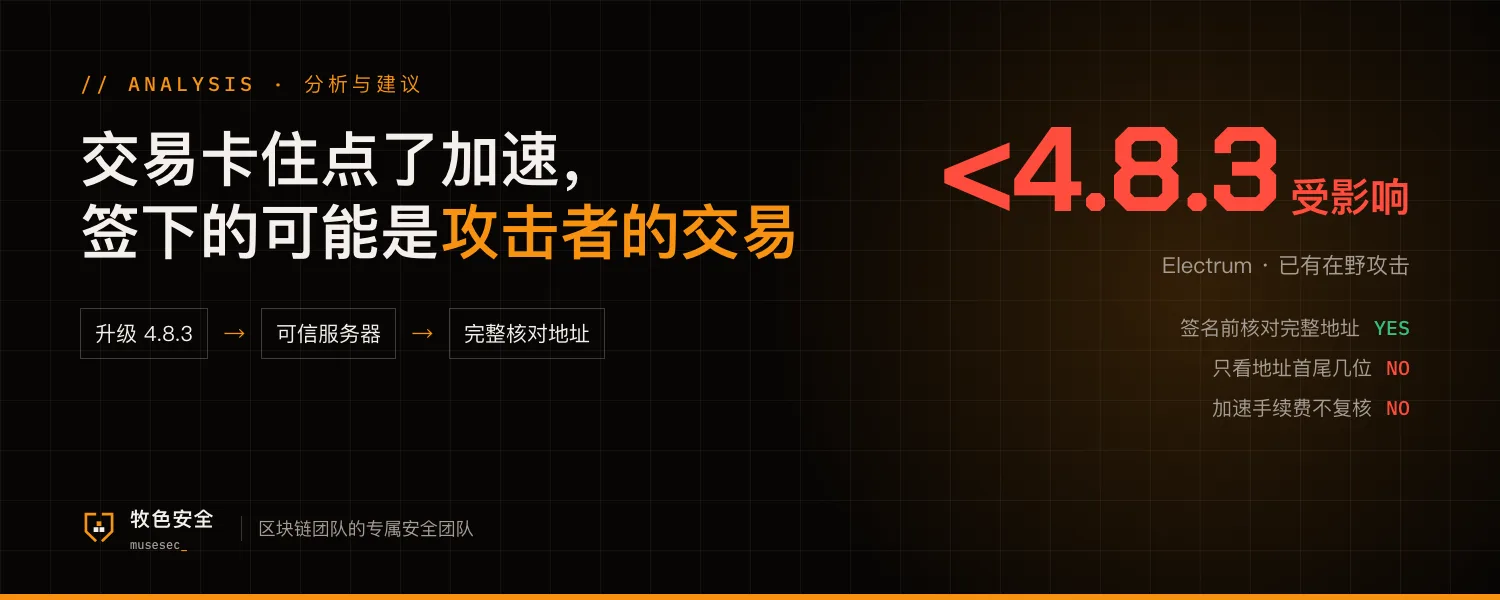
Electrum Flaw Exploited in the Wild: The Fee Bump You Sign May Pay the Attacker

On October 24, Electrum published a high-severity advisory: versions before 4.8.3 do not verify signatures on unconfirmed transactions supplied by the server, so a malicious server can swap the destination address and trick users into signing a fee bump that pays the attacker. Attacks have been seen in the wild. What it means for blockchain teams of 10 to 50 people, viewed through process, risk and privileges, with five steps to take now.

#Wallets & signing

Read article →
Retiring an address does not close the incident when its leaked key still receives funds

Analysis

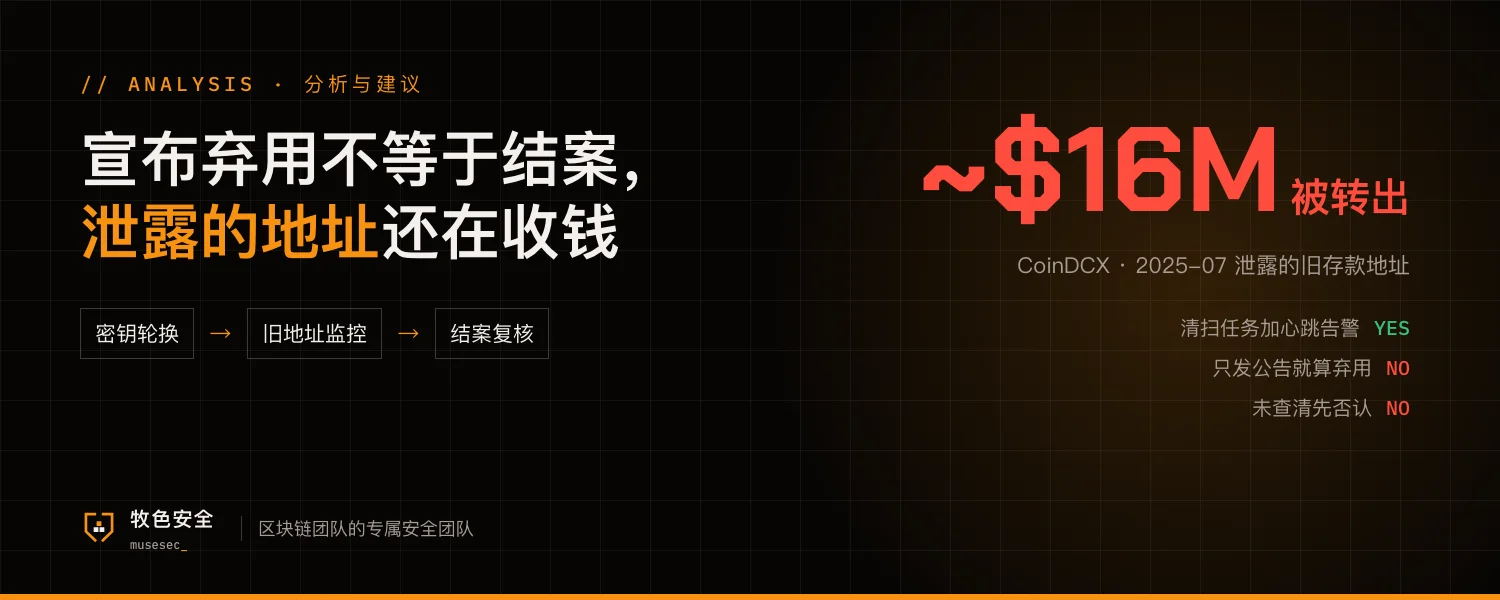
CoinDCX's Retired, Compromised Deposit Addresses Kept Receiving Funds: Five Steps to Close Out an Incident

On October 22, about $16M was flagged leaving addresses linked to CoinDCX. The exchange says the keys for these deposit addresses were exposed in its July 2025 incident and the addresses were retired, yet users kept depositing and a sweep process failed for a period. What it means for blockchain teams of 10 to 50 people, viewed through process, risk and privileges, with five steps to take now.

#Exchange & funds#Wallets & signing

Read article →
When your deployment platform is breached, private keys should not be in its environment variables

Analysis

Railway Environment Variable Breach Drains Stored Private Keys: Five Things Small Teams Should Do

On October 21, cloud deployment platform Railway disclosed unauthorized access to the systems that store customer environment variables. According to security researchers, about $371K was then swept from more than 200 addresses. What it means for blockchain teams of 10 to 50 people, viewed through process, risk and privileges, with five steps to take now.

#Wallets & signing#Servers & infrastructure

Read article →

INCIDENT RESPONSE · ASSESSMENT

Fix the gaps before attackers find them

Reply within 24 business hours · [email protected]

CONTACT

Tell us about your situation

Leave your contact details and needs and we will get back to you soon. You can also reach us on WeChat.

WeChat QR
WeChat